Enterprise AI agents need a middle ground between raw, risky database access and total lockdown that makes them useless—a trust layer of centralized governance and policy controls that gives agents exactly the data access they need, no more.
Key Takeaways
- Trust3 AI’s integration with Snowflake-managed MCP servers lets you expose governed, ready-to-use AI data to agents in minutes, without building or maintaining separate MCP infrastructure.
- Business-aligned access: agents get clean, logical data products (like “Customer Data”) instead of raw physical tables.
- Dynamic policy control: access rules are enforced based on tags and context, not hardcoded into brittle schemas.
- Zero infrastructure overhead: Snowflake manages the MCP server while Trust3 AI governs the access, reducing the risk of tool poisoning and unauthorized data exposure.
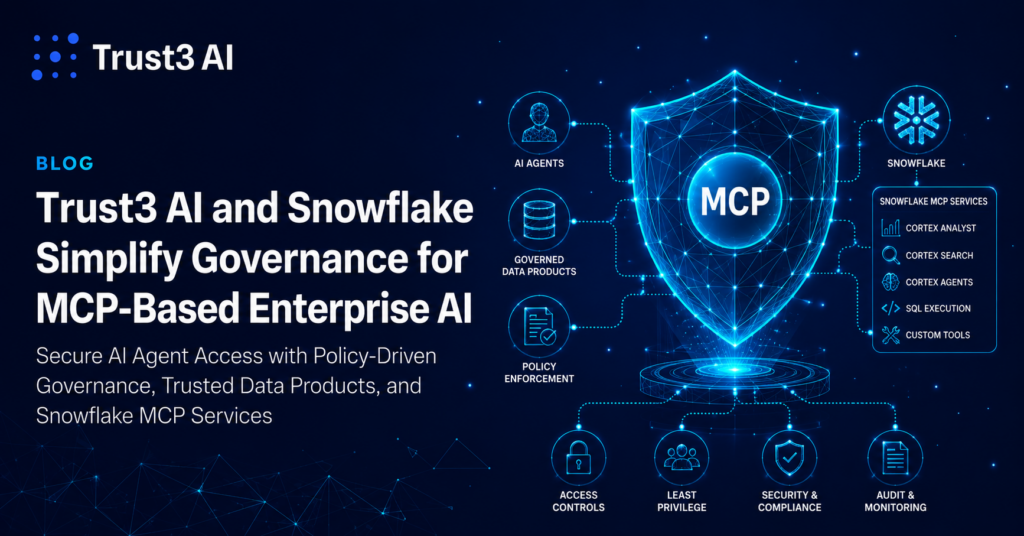
That is exactly why we built our new integration with the Snowflake AI Data Cloud. By combining our policy-driven governance with Snowflake-managed Model Context Protocol (MCP) servers, you get governed, ready-to-use AI data. That is, you can now safely expose governed data to your AI agents in minutes. You get full security and scalability right out of the box, completely eliminating the burden of building and maintaining separate MCP infrastructure.
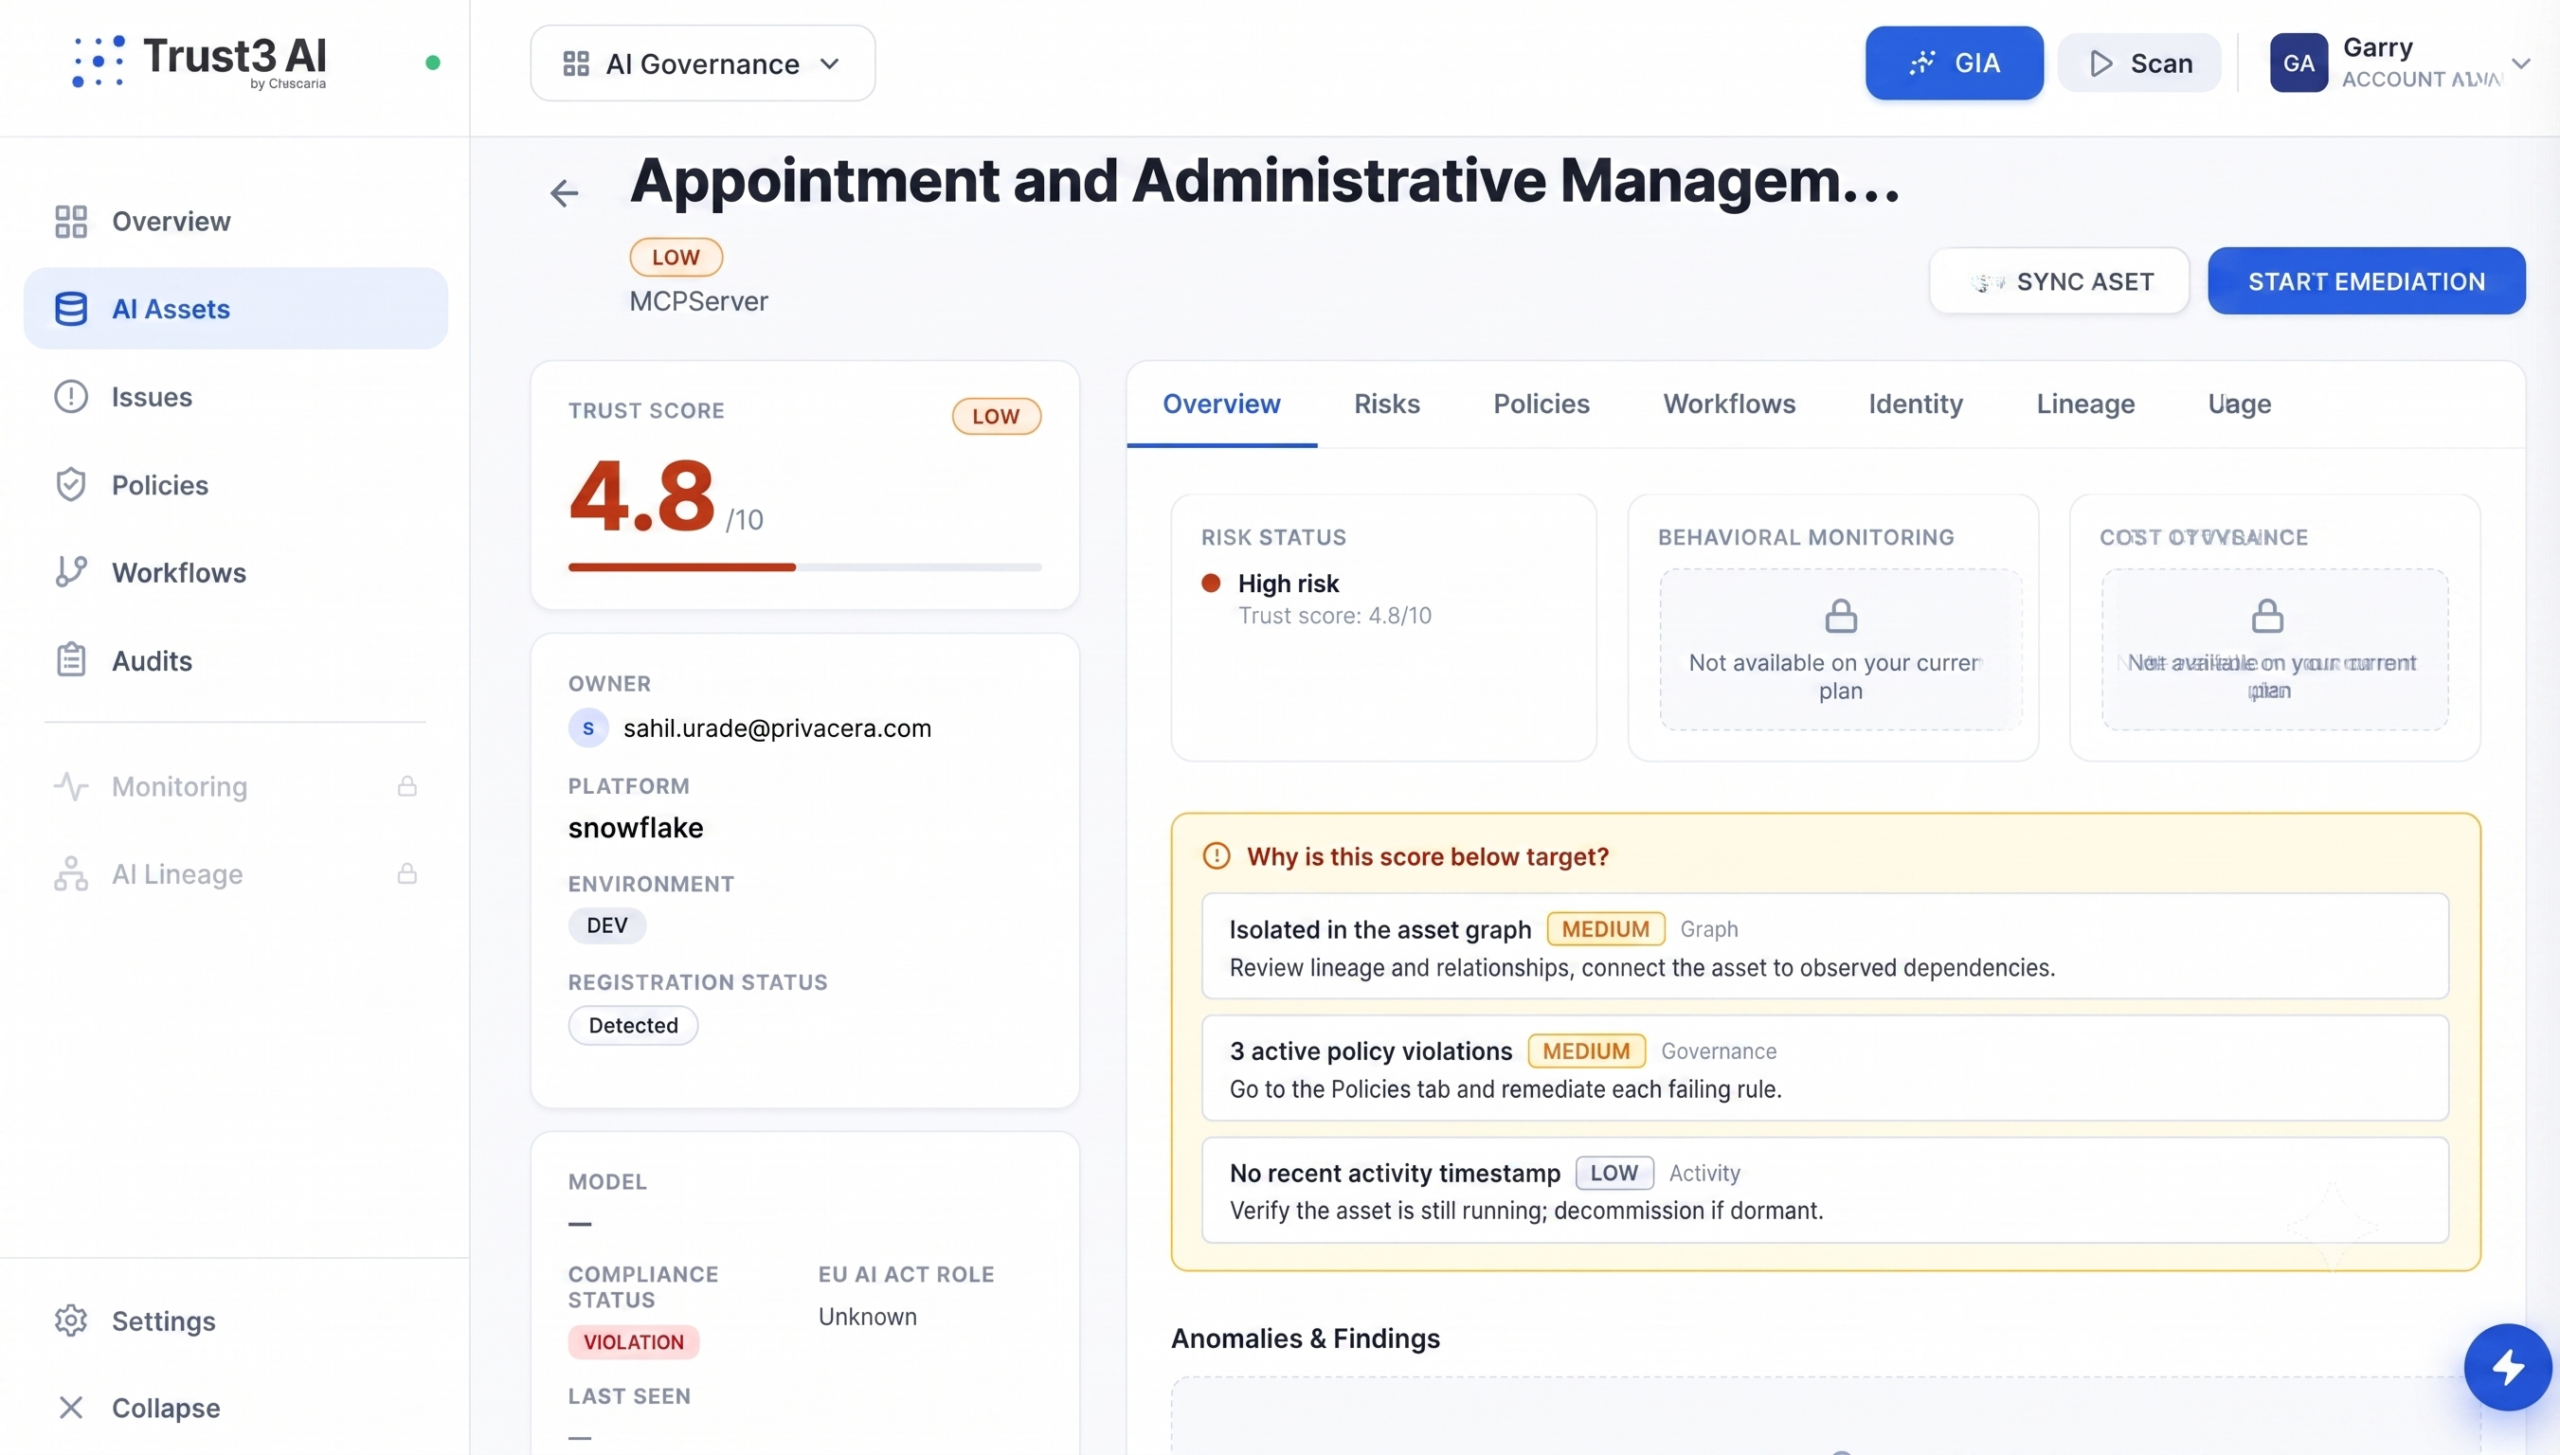
The Problem with Raw Schemas
Giving agents direct access to raw physical data assets is a recipe for chaos. It bypasses business logic and ignores user context.
Our integration flips this outdated model. At the core is a data-product-centric model for AI access. Instead of exposing raw tables, Trust3 AI lets you present governed business data to agents as logical products. Think of reusable, business-aligned views like “Customer Data” or “Transaction Logs.”
By abstracting the underlying schemas, you create a safer environment. Access restrictions apply dynamically based on user context, data attributes, and legal obligations rather than being hardcoded into brittle data definitions.
Governed MCP-Based Data Access
Snowflake recently introduced managed MCP servers. This architecture allows organizations to configure Cortex Analyst, Cortex Search, Cortex Agents, and custom tools behind a standards-based MCP interface. It includes built-in OAuth authentication and role-based access control.
Trust3 AI extends these powerful capabilities. We map your approved data products directly to MCP-accessible resources. You manage how agents discover tools and invoke data services under one centralized policy.
This setup heavily emphasizes least-privilege access. You can configure separate privileges for connecting to an MCP server versus actually invoking the underlying tools. It is a fine-grained authorization model designed specifically for modern agentic workflows.
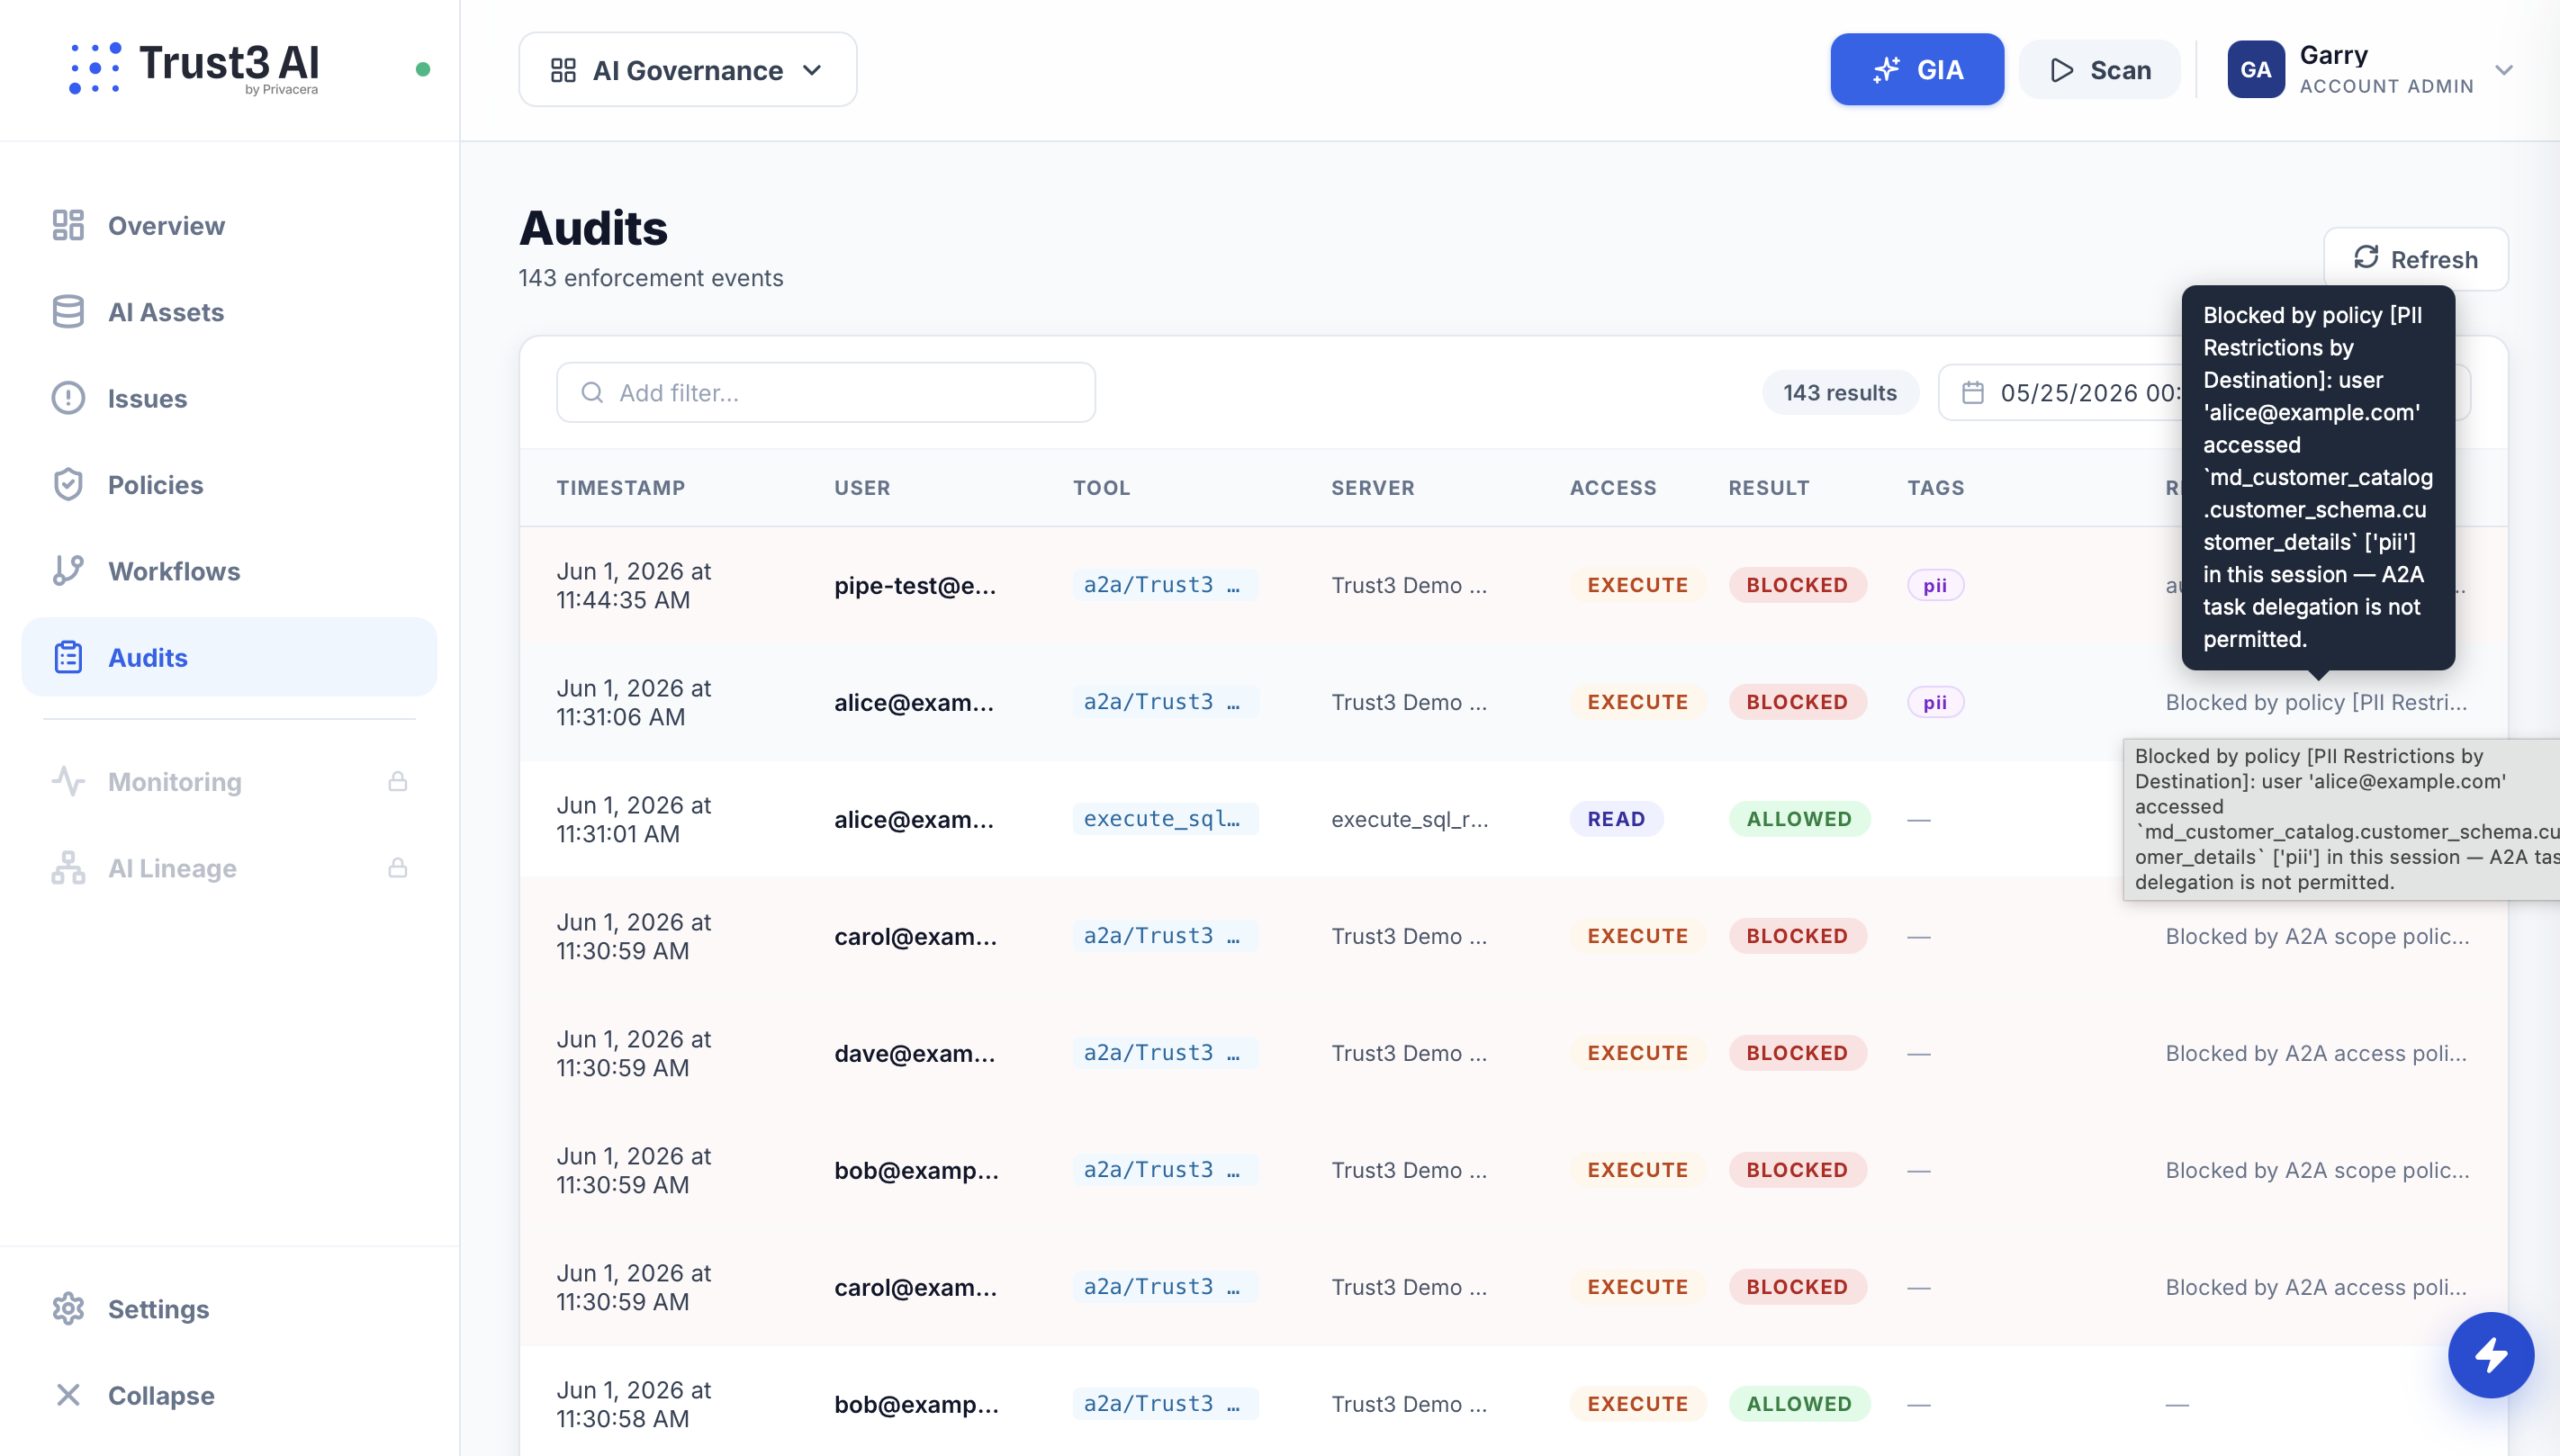
Scaling Trusted AI Experiences
This integration also fully supports Snowflake Intelligence. When your teams interact with structured and unstructured enterprise data using natural language, Trust3 AI adds a crucial governance layer. Every interaction automatically inherits consistent policy enforcement and access mediation.
Here is why this matters for your engineering and data teams:
- Business-aligned access: You present agents with clean, logical data products instead of exposing them to raw physical storage.
- Dynamic policy control: You enforce rules based on tags and context.
- Zero infrastructure overhead: Snowflake manages the MCP server while Trust3 AI governs the access.
- Safer operations: You reduce the risk of tool poisoning and unauthorized data exposure through strict least-privilege permissions.
Build Faster with Confidence
Enterprise AI demands more than simple connectivity. It requires absolute trust. By pairing Trust3 AI with the Snowflake managed MCP architecture, you can give your agents the precise data they need to be effective. You maintain complete control over authorization and policy enforcement at every step.
You no longer have to choose between moving fast with AI and keeping your data secure. Now you can do both.
Frequently Asked Questions
What does Trust3 AI’s integration with Snowflake-managed MCP servers do?
It lets teams expose governed, ready-to-use AI data to agents in minutes, without building or maintaining separate MCP infrastructure. Agents get clean, logical data products, like “Customer Data,” instead of raw physical tables, and access rules are enforced dynamically based on tags and context rather than hardcoded into brittle schemas.
How is this different from giving AI agents direct access to raw Snowflake tables?
Giving agents direct access to raw physical data bypasses business logic and ignores user context. Trust3 AI’s data-product-centric model instead presents governed, business-aligned data products to agents, reducing the risk of tool poisoning and unauthorized data exposure.
Who manages the infrastructure for this governance layer?
Snowflake manages the MCP server itself, while Trust3 AI governs the access, so there is zero additional infrastructure overhead for teams adopting this approach.
More from Trust3 AI
- From Snowflake Keynote Vision to Cross-Platform Reality: Securing the Agentic Enterprise
- Snowflake Summit 2026 Day 2: The AI Experiment Is Over. The Agentic Enterprise Has Arrived
- Fuel Up at Trust3 AI’s Coffee Truck at Snowflake Summit and Learn How to Secure Your Agents in a Growing Environment
- Trust3 AI and Snowflake on August 25: Who’s Governing Your Agents?
- Governed Access to Any Source From OneLake
- Trust3 AI Launches Native App on Snowflake Marketplace to Secure Enterprise AI
Related Articles